Interactive Brokers finally supports passkeys

missaq

New member
I randomly found out last week that Interactive Brokers now supports passkeys, including hardware security keys like YubiKeys.

Honestly, I am really happy to see this. For a brokerage account, having the option to use a hardware backed passkey is a big security improvement in my opinion. It is also much more convenient than relying on passwords and traditional 2FA methods.

I was not even aware that IBKR had added support for this, so I figured I would share it here in case others missed it too.

Nice to see Interactive Brokers finally adding passkey support.
 
Hi and welcome to the forum!

That's amazing news, I did not see this either.

I know they supported 2FA TOTP which is what I was using, but yubikey is another level of security. I really wish more and more services were opting for such levels of security. In Switzerland, we are mostly stuck with SMS 2FA.

I will try it out, thanks for sharing!
 
Hi and welcome to the forum!

That's amazing news, I did not see this either.

I know they supported 2FA TOTP which is what I was using, but yubikey is another level of security. I really wish more and more services were opting for such levels of security. In Switzerland, we are mostly stuck with SMS 2FA.

I will try it out, thanks for sharing!

Thanks! I registered two YubiKeys on my account, just to have a backup.

One thing I noticed is that if you want to disable the IB Key, you need to create a support ticket. I would probably just call them directly though, as that seems to be the easier option.

Glad you found the post useful!
 
Hi

Where did you find this option?
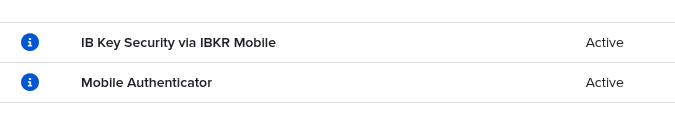
I expected it to find it under Secure Login System but I only see mobile authenticator and IB key there.
 
Hi

Where did you find this option?
I expected it to find it under Secure Login System but I only see mobile authenticator and IB key there.
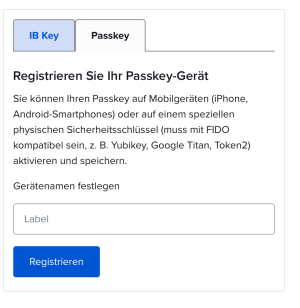
Yes, it is under the Secure Login System, and then you see the tab "Passkey," and there you can add your keys.
 

Attachments

  • Bildschirmfoto 2026-09-14 um 17.39.36.png
    Bildschirmfoto 2026-09-14 um 17.39.36.png
    95.9 KB · Views: 3
This is very interesting, and I would like such a system (I don't like being too dependent on my phone). However, a few days ago I read about how the "Coldcard" crypto wallet hardware was breached. The system that generated random passwords... wasn't truly random, so they managed to access various wallets and steal several million dollars in BTC. This makes me wonder if something similar could happen with Passkeys.

I am writing as someone ignorant about IT in a forum where I know there are many experts, so please don't beat me up if I've made a silly association :P
 
It's very good to be skeptic about these things. It's entirely true that there could be some software (or even hardware) issue.

Usually, there is a private part and a public part. The public part is enough to verify a new passkey but not enough to generate it. This is a system similar to that of HTTPS which is used everywhere. The system itself is sound, but again, the true quality comes from the implementation.

I have not been aware of any issues with passkeys. The best type of passkeys are passkeys where the private part is not stored on your device but instead stored on an hardware key (like Yubikey). They have been around for a while and I consider them safe.

In the case of coldcard, they did a mistake in their code that allowed this. A yubikey is more locked down than a Coldcard. But yes it could happen. Unfortunately, we have to trust to some level. And this is only the second factor. So even if they broke the second factor, they would still need to figure out your password which needs to remain strong.
 
Back
Top